Audit and compliance

ENISA has published a guide for software component inventorying

November 2, 2026 1 min read
enisa

On October 22, 2026, ENISA published a practical guide for SBOM adoption: the Software Bill of Materials. The document specifically targets SMEs and aims to increase transparency in the software supply chain.

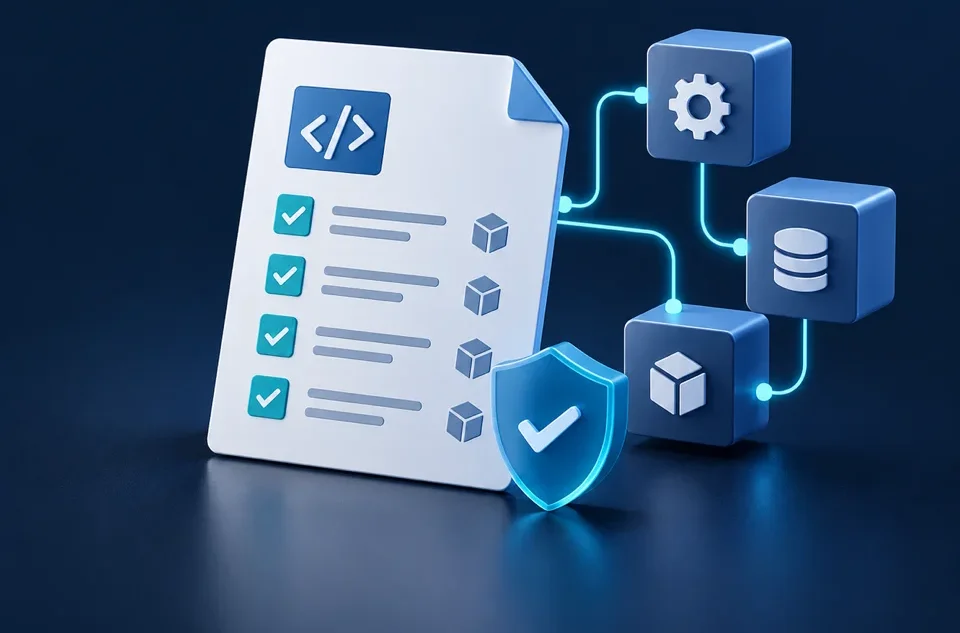
The guide covers the architecture, data flows, and security measures required throughout the SBOM lifecycle. The goal is to transform component information into decisions regarding suppliers and security priorities.

Three practical measures to consider:

  • Include the availability of a component inventory and its update process in your supplier evaluations.
  • Establish who verifies the information received, who tracks dependencies, and who approves remediation measures.
  • Protect the integrity of and access to the inventory; use it in risk assessments alongside product security checks.

Dataeye Consulting can support the evaluation of procurement processes and security controls for software dependencies.
Articles you might also be interested in

Glob digital format dintr-o rețea de puncte luminoase

Audit, penetration testing or consulting: where do you start?

Three services, three different questions: where do I stand, what could happen and what do I do next. Here is how to choose the right starting point for your organisation.
October 28, 2026 3 min read
Scut de securitate cu bifă și stelele Uniunii Europene

NIS2 in brief: what it means for organisations in Romania

NIS2 sets clear cybersecurity requirements for organisations in essential and important sectors. Here is what the directive covers and how to prepare in practice.
October 21, 2026 2 min read
Puzzle alb cu o piesă lipsă, pe fundal negru

What is a gap analysis and when does it make sense?

A gap analysis compares what you have now with what you should have. Here is how it works, how maturity is measured and what you get at the end.
October 14, 2026 2 min read